Setting up a Salesforce OAuth Connection
Salesforce connections can be configured using OAuth. A single connector can be used to connect to both a Sandbox and Production Instance.
SmartConnect supports two OAuth authentication methods:
- JWT Bearer Flow (recommended) – Authenticates server-to-server using a digital certificate. There is no sign-in prompt and no refresh token to expire, which makes it the best choice for scheduled and unattended integrations.
- Authorization Code Flow – Authenticates by signing in to Salesforce and allowing access. Supports PKCE, which Salesforce requires for all External Client Apps created after June 25, 2026.
Set up in Salesforce
Before adding the Salesforce connector, we need to create an app in Salesforce.
Find Salesforce Instance
- Log into the Salesforce environment as the user.
- Open Setup and search for Company Information.
- Locate the Instance value and save it for later.

Find Salesforce Domain Name
- Log into the Salesforce environment as the user.
- Open Setup and search for My Domain.
- Locate the Current My Domain URL value and save it for later.
- Ensure that the option under Login Policy, “Prevent login from {{url}},” is unchecked if we want to allow authentication using {{url}}. If we want to prevent login from {{url}}, we need to use the My Domain URL in the Service URL section.

JWT Bearer Flow (recommended)
The JWT Bearer Flow authenticates using a certificate generated by SmartConnect. There is no sign-in prompt and no refresh token to expire.
Create an App in Salesforce
- Log into the Salesforce environment as the user.
- Open Setup and search for App Manager.
- Select New External Client App.
Apps are unique for each environment/sandbox.

- External Client App Name – Friendly name for the app.
- Contact Email – Email address for app issues/validation, and Keep Distribution State – Local
- Enable OAuth Settings – Box must be selected.
- Callback URL – A Callback URL must be entered even though the JWT Bearer Flow does not use it. Salesforce requires a value to save the app. Any valid URL that starts with http:// or https:// can be used, such as https://login.salesforce.com/services/oauth2/success or https://localhost. It does not need to point to a live endpoint.
- Selected OAuth Scopes – Choose these 5 scopes.
- Access the identity URL service (id, profile, email, address, phone)
- Manage user data via APIs (api)
- Manage user data via Web browsers (web)
- Perform requests at any time (refresh_token, offline_access)
- Access custom permissions (custom_permissions)


- Click Create. The JWT Bearer Flow is enabled later, after the certificate is generated in SmartConnect.
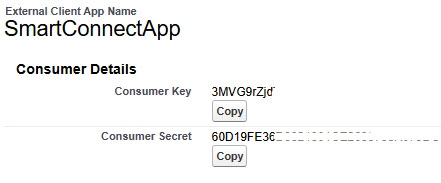
- Go to App >> Settings Tab, click Consumer Key and Secret. If you are prompted to enter a code to verify your identity, please retrieve the code from the email address entered in Step 5.

- On the next screen save the Consumer Key for use later. The JWT Bearer Flow does not use the Consumer Secret.
Setting up the connector in SmartConnect
- Login to login.smartconnect.com.
- Navigate to Connections > Create Connection button (or edit an existing Salesforce connection).
- Select Salesforce.
- SandBox/Production – Use tabs to configure Sandbox and Production connections in a single connector.
- Description – Friendly name for the connection.
- Api Version – Salesforce API version used by the connection. Defaults to 48.
- Create Tests – If selected, SmartConnect will create the necessary apex tests to promote your sandbox objects to production.
- Authentication – Select OAuth JWT Bearer.
- Service URL –
- Use:
https://login.salesforce.com/services/oauth2→ for Production/Developer, orhttps://test.salesforce.com/services/oauth2→ for Sandbox - If login from {{url}} is prevented under My Domain, use your My Domain URL instead:
https://<mydomain-url>.my.salesforce.com/services/oauth2, where <mydomain-url> is the value found at the start of this article. Organizations that use SSO or other My Domain login restrictions also require the My Domain URL.
- Use:
- Organization Name – Read-only name of Organization (Populated after click Validate).
- Organization Type – Read-only Type of Organization (Populated after click Validate).
- Under External Client App — JWT bearer, complete the Default Security fields.
- Consumer Key – Consumer Key from Salesforce Setup.
- Salesforce Username – Username of the Salesforce user the connection runs as. This user is pre-authorized in the App Policies section below.
- Signing Certificate – Select how long the certificate is valid (for example, 2 years) and click Generate Certificate. Generating a certificate saves the connection first.
- Click Download and save the certificate file.
- Administration Security (optional) – Leave the Consumer Key blank to use the Default Security app for administration too. To use a separate app for administration, enter its Consumer Key and Salesforce Username.
Enable the JWT Bearer Flow in Salesforce
- In Salesforce, open Setup and search for App Manager.
- Select your External Client App, open the Settings tab, and click Edit under OAuth Settings.
- Flow Enablement – Check Enable JWT Bearer Flow, click Upload Files, and select the certificate downloaded from SmartConnect.
- Click Save.
Set up the App Policies (required)
This step is required for the JWT Bearer Flow. Because there is no prompt to allow access, Salesforce only accepts the connection if Permitted Users is set to Admin approved users are pre-authorized and the Salesforce Username entered in SmartConnect is assigned one of the app’s selected profiles or permission sets. This user needs the API Enabled permission and access to the objects used in your integrations.
- Open Setup and search for Permission Sets.
- Create a permission set for the integration (or use an existing one) and assign it to the user.
- Open App Manager, select your External Client App, and open the Policies tab.
- Click Edit.
- Under Plugin Policies, set Permitted Users to Admin approved users are pre-authorized.
- Under App Policies, move the permission set (or the user’s profile) to the selected list.
- Click Save.
Validate the connection
- Return to the Salesforce connection in SmartConnect.
- Click Validate. No prompt is displayed.
- Save the Connector.
Note – If validation fails with “user hasn’t approved this consumer,” confirm the user is assigned the permission set selected on the app’s Policies tab.
Authorization Code Flow
The Authorization Code Flow authenticates by signing in to Salesforce and allowing access. Salesforce requires PKCE on all External Client Apps created after June 25, 2026.
Create an App in Salesforce
- Log into the Salesforce environment as the user.
- Open Setup and search for App Manager.
- Select New External Client App.
Apps are unique for each environment/sandbox.
- External Client App Name – Friendly name for the app.
- Contact Email – Email address for app issues/validation, and Keep Distribution State – Local
- Enable OAuth Settings – Box must be selected.
- If you are using SmartConnect.com, please enter the correct Callback URL based on your deployment/region.
- Navigate to Connections > Create Connection > Salesforce.
- Set Authentication to OAuth and copy the redirect URL displayed in the connection window.
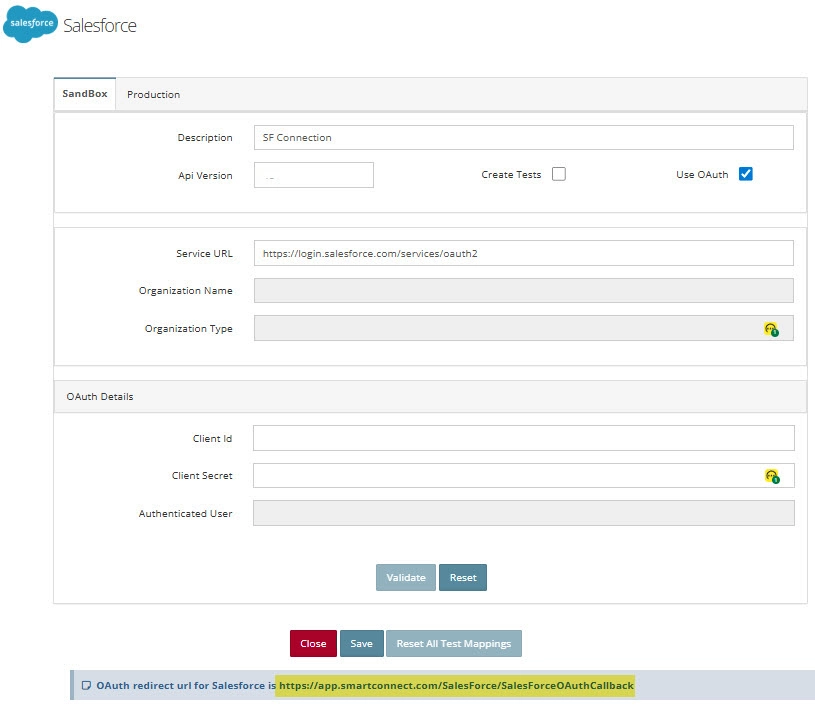
Note – If you are using SmartConnect 21 on-premises, please enter the correct Callback URL. Navigate to Connections > Create Connection > Salesforce and set Authentication to OAuth and copy the redirect URL displayed in the connection window.
If you want to use multiple callback URLs, you can add them by entering the first URL on the first line and the second URL on the next line.
- Selected OAuth Scopes – Choose these 5 scopes.
- Access the identity URL service (id, profile, email, address, phone)
- Manage user data via APIs (api)
- Manage user data via Web browsers (web)
- Perform requests at any time (refresh_token, offline_access)
- Access custom permissions (custom_permissions)
- Flow Enablement – Check Enable Authorization Code and Credentials Flow.
- Security – Require Proof Key for Code Exchange (PKCE) Extension for Supported Authorization Flows must be selected for new apps. If this box is selected, you must check Use PKCE when setting up the connector in SmartConnect.
- Click Create.
- Go to App >> Settings Tab, click Consumer Key and Secret. If you are prompted to enter a code to verify your identity, please retrieve the code from the email address entered in Step 5.
- On the next screen save the Consumer Key and Consumer Secret for use later.
Also, please verify the OAuth Policies under the Policies tab and ensure that the default settings remain unchanged. If needed, you may change the refresh token policy to “Refresh Token is Valid Until Revoked” based on your business requirements. However, Salesforce generally recommends using the “Expire refresh token after a specified time” option, commonly set to 90 days, for better security.

Setting up the connector in SmartConnect
- Login to login.smartconnect.com.
- Navigate to Connections > Create Connection button (or edit an existing Salesforce connection).
- Select Salesforce.
- Sandbox/Production – Use tabs to configure Sandbox and Production connections in a single connector.
- Description – Friendly name for the connection.
- Create Tests – If selected, SmartConnect will create the necessary apex tests to promote your sandbox objects to production.
- Authentication – Select OAuth Client Credentials.
- Use PKCE – Check this box if PKCE is required on the Salesforce app. This is required for apps created after June 25, 2026.
- Service URL –
- Use:
https://login.salesforce.com/services/oauth2→ for Production/Developer, orhttps://test.salesforce.com/services/oauth2→ for Sandbox - If login from {{url}} is prevented under My Domain, use your My Domain URL instead:
https://<mydomain-url>.my.salesforce.com/services/oauth2, where <mydomain-url> is the value found at the start of this article. Organizations that use SSO or other My Domain login restrictions also require the My Domain URL.
- Use:
- Organization Name – Read-only name of Organization (Populated after click Validate).
- Organization Type – Read-only Type of Organization (Populated after click Validate).
- OAuth Details
- Client Id – Consumer Key from Salesforce Setup.
- Client Secret – Consumer Secret from Salesforce Setup.
- Reset All Test Mappings – Reset all configured Test Class mappings to their default values.

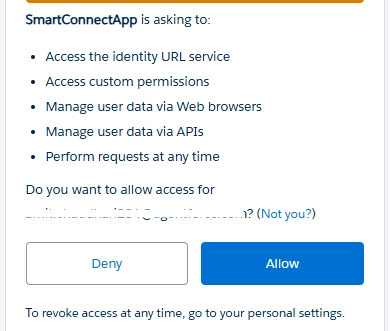
- Click Validate and Allow the prompt for access.
- Save the Connector.
Note – Existing connections using apps created on or before June 25, 2026 continue to work without changes. If you enable PKCE on an existing app, edit each connection that uses it, check Use PKCE, and click Validate.